All Categories
Featured

Leveraging Performance Metrics to Improve Cloud ROI
Table of Contents
By keeping an eye on cloud resources and their associated expenses, companies can make educated choices that line up with their financial and strategic goals. In essence, cloud possession management isn't just a side componentit's a cornerstone of digital improvement strategies. It makes sure that companies can scale efficiently, control expenses, and preserve the dexterity needed to adjust to ever-changing market demands.
Impact of Strict Governance On 2026 Cloud BudgetsManaging cloud possessions is essential for companies due to: Preventing over-provisioning and getting rid of unused cloud resources. Getting insights into cloud usage and avoiding shadow IT.
By leveraging these combination choices, businesses can enable single sign-on (SSO) for cloud-hosted work. This streamlines authentication, letting users gain access to resources with their familiar qualifications while keeping central identity management. The secret is to configure IAM manages so that roles and permissions mirror only what each user needsadhering carefully to the concept of least opportunity.
To protect sensitive information in the cloud, organizations need to implement robust file encryption both in transit and at rest. Think about these tested approaches: Use industry-standard protocols such as TLS (Transportation Layer Security) to encrypt information as it moves in between devices and cloud services. Safe and secure data at rest using algorithms like AES-256, making sure files remain protected even if storage resources are jeopardized.
Streamlining IT Resources to Maximize Corporate Efficiency
By applying these strategies, companies can significantly enhance their data security posture in any cloud environment. To reinforce cloud border security beyond fundamental procedures, organizations can utilize a range of specialized tools.
These tools supply deep packet evaluation, evaluate network traffic for indications of destructive activity, and can immediately react to obstruct or inform on risks as they occur. For even higher visibility, think about solutions that use real-time traffic analysis and habits tracking. This proactive approach helps detect abnormalities and possible breaches early, strengthening your protective border.
An important piece in the cloud security puzzle is the shared obligation model. This framework clearly marks where the cloud provider's security tasks end and where yours beginthough the boundaries shift depending upon your chosen cloud service model: Facilities as a Service (IaaS), Platform as a Service (PaaS), or Software Application as a Service (SaaS).
Why Cloud Management Remains Essential for 2026 ROI
You, the consumer, are responsible for securing everything you construct atop that facilities. This spans from installing OS spots and managing network security manages to configuring firewall programs and protecting your virtual makers with malware protection.: With PaaS, the supplier extends their protective reach to consist of the platform itselfthink managed operating systems and middleware.
You'll require to impose strong access controls, safe sensitive details, and monitor your hosted applications.: SaaS environments offload the bulk of security management to the service provider. They're tasked with securing the application stack, underlying operating systems, and network settings. Your primary focus shifts to securing user gain access to, handling use policies, and securing your organization's data within the application.
Leverage both integrated and third-party security tools to fortify the locations under your control. Keep access policies, keeping an eye on practices, and information security procedures as much as date, no matter your cloud intake model. Cloud security isn't one-size-fits-all, but with a clear grasp of your role in this collaboration, you set the phase for a much safer, more durable environment in the cloud.
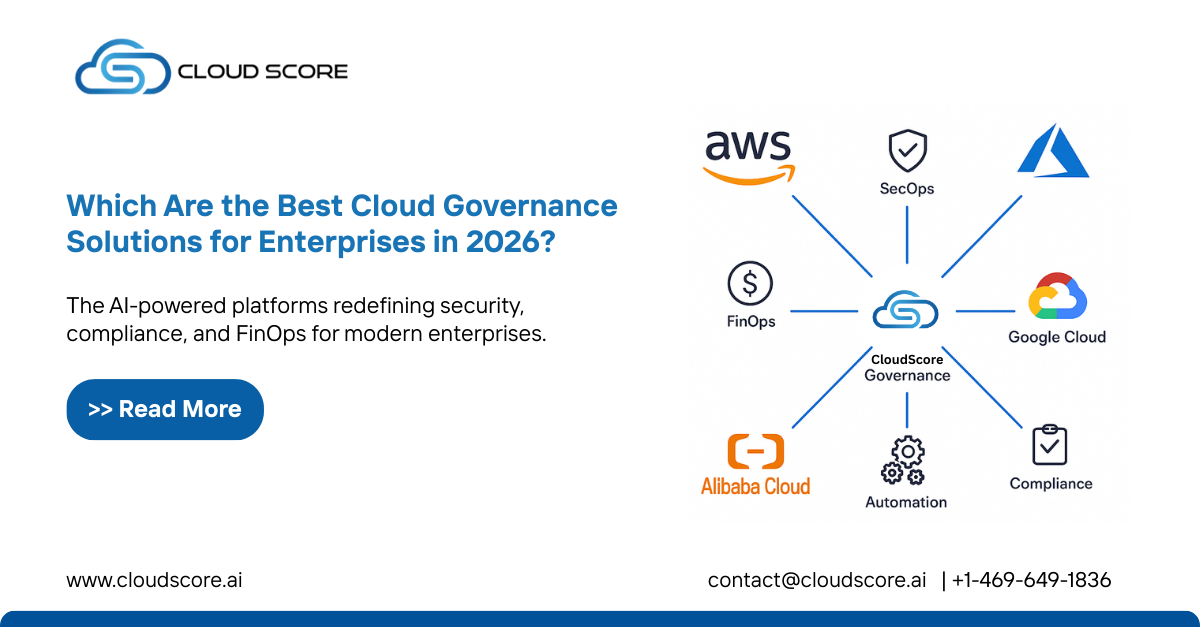
Rather of handling a patchwork of disparate toolseach with its own dashboard and discovering curvesecurity groups gain one thorough view into endpoints, work, identities, and data security. This consolidation reduces intricacy, making it much easier to track possible risks as they unfold, without the need to hop between various user interfaces to get the complete picture.
Streamlining IT Resources to Increase Corporate Efficiency
By handling defenses, monitoring, and policy implementation from a main console, groups are empowered to carry out consistent security measures throughout accounts, regions, and projects in one go. This approach lessens the overhead of managing multiple licenses, lessens administrative burden, and makes sure policies are imposed evenly. Eventually, combining security controls enhances visibility, performance, and agilitycore active ingredients for keeping rate with developing cloud needs.
Impact of Strict Governance On 2026 Cloud BudgetsInstead of leaving groups to rush in the middle of chaos, these strategies provide a clear course of action ought to an event take place. With predefined responsibilities and structured workflows, everybody knows their rolethink of it as assigning seats on a lifeboat before the storm strikes. Having this structure in place yields several essential benefits: Immediate and collaborated action helps include risks before they mushroom.

Latest Posts
How to Optimize Infrastructure ROI With Better Metrics
Analyzing IT Performance Through Advanced Governance Metrics
Key Strategies for Modern Budget Planning